
Origin Security
The Origin Security feature in AppNavi enhances security by allowing you to restrict access to your application's resources, including APIs and data files, based on the originating domain (origin). It helps you control which external domains can communicate with your application, ensuring that only trusted domains have access to your resources.
This feature can be enabled or disabled at the app level, with default settings keeping it deactivated. When enabled, you can define up to 10 allowed origins, including specific domains and wildcard patterns for flexible control over who can access your application.
Overview
What is Origin Security?
Origin Security is a domain-based access control mechanism that restricts which external websites and applications can access your AppNavi resources. When enabled, only requests from approved origins (domains) can access your application's APIs, data files, avatars, and other resources.
Key Benefits
• Domain-Level Access Control - Restrict resource access to specific trusted domains
• API Protection - Prevent unauthorized API calls from untrusted origins
• Static Resource Protection - Control access to data files, images, and multimedia
• Wildcard Flexibility - Use wildcard patterns to allow entire subdomain trees
• Simple Configuration - Define up to 10 origins with intuitive pattern matching
• Default Security - Disabled by default; enable only when needed
• Seamless Integration - Works with or without tenant-level encryption
• Avatar & Resource Security - Restrict avatar display and resource serving by origin
Prerequisites
Before configuring Origin Security, ensure you have:
• Admin or application management permissions in AppNavi
• Access to the Manage Tenant section
• Understanding of domain names and URL structure
• Knowledge of your application's expected integration origins
• Ability to identify subdomains and wildcard patterns
• List of authorized external domains that need access
When to Use Origin Security
Enable Origin Security in these scenarios:
• Your application is embedded on external websites and you want to restrict who can embed it
• You need to control API access to your application from specific domains only
• You want to prevent competitors or unauthorized parties from using your resources
• You are implementing direct integration and want to protect against domain hijacking
• You need to comply with security policies requiring domain-based access control
• You have multiple development, staging, and production environments with different origins
Understanding Origins & Patterns
What is an Origin?
What is an Origin?
An origin is the combination of protocol (http:// or https://), domain name, and optional port. For example, https://example.com, https://app.example.com, and https://example.com:8080 are three different origins.
Pattern Matching Rules
Origin Security uses pattern matching to determine which origins are allowed:
Exact Match: https://example.com matches only https://example.com, not subdomains
Wildcard Match: https://*.example.com matches https://app.example.com and https://api.example.com
Multi-Level Wildcard: .example. matches https://sub.example.com and https://sub.example.org
Protocol Required: https://example.com does NOT match http://example.com (different protocols)
Port Specific: https://example.com:8080 does NOT match https://example.com (different ports)
How to Configure Origin Security
Step 1: Navigate to Application Settings
- Sign in to your AppNavi account with admin permissions
- Navigate to the Manage Tenant section from the main menu
- Click on the Applications tab to view all applications
- Click the + icon to create a new application OR select an existing application to edit
- Confirm you are in the application settings/configuration area
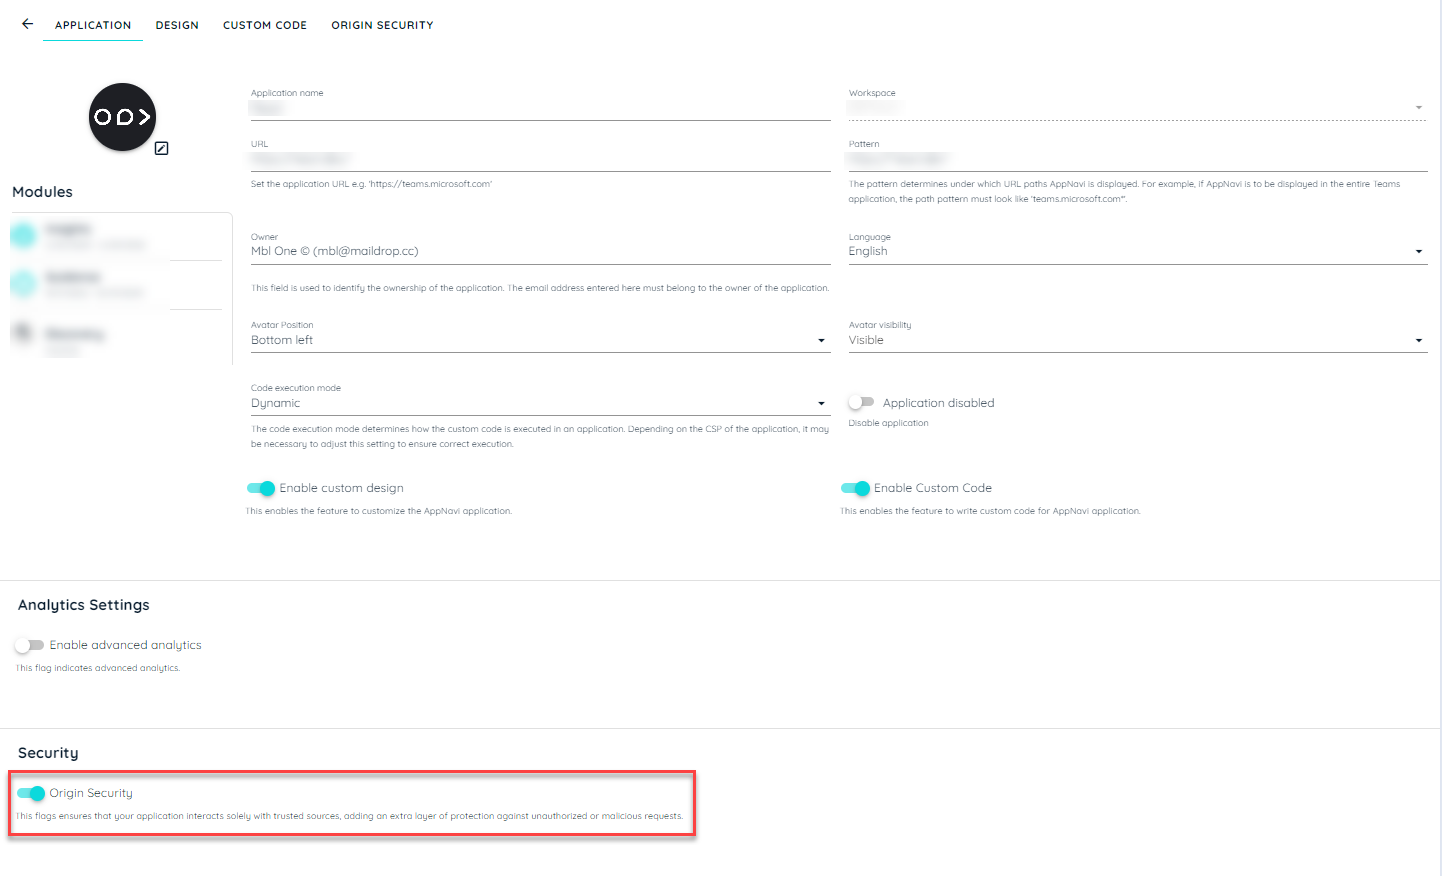
Navigate to Manage Tenant > Applications tab and select an application to access Origin Security.
Step 2: Enable Origin Security Toggle
- Locate the "Origin Security" toggle button in the application settings
- Origin Security starts in the disabled state for all new applications
- Click the toggle switch to turn on Origin Security
- After enabling, verify the toggle shows as "ON" or "Enabled"
- Once enabled, a new tab labeled "Origin Security" will appear in the settings
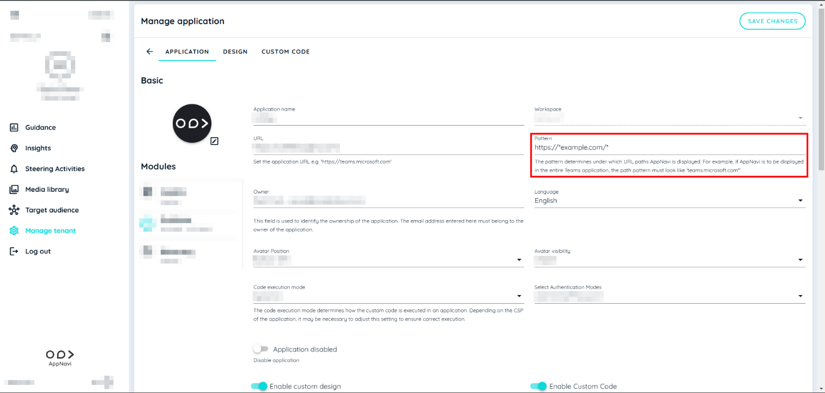
Toggle the Origin Security switch ON; a new Origin Security tab will appear in the application settings.
Step 3: Configure Allowed Origins
- Click on the "Origin Security" tab that appeared after enabling
- You will see a form or input area for adding allowed origins
- Click "Add Origin" or similar button to add your first allowed domain
- Type your domain pattern (e.g., https://example.com or https://*.example.com)
- Ensure pattern starts with http://, https://, or *.
- Repeat the process to add up to 10 allowed origins
- Click "Save" or "Apply" to persist your origin settings
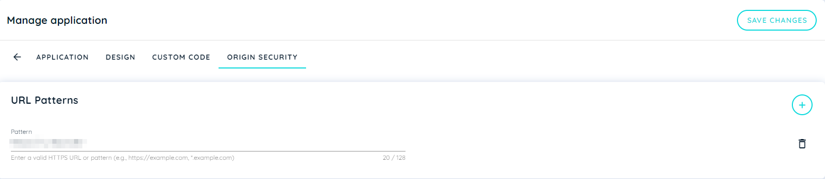
Specify exact domains or use wildcards for subdomains in the Origin Security tab
Valid & Invalid Origin Patterns
Pattern Format Requirements
When defining origin patterns, follow these rules:
Protocol Required: Patterns must start with http://, https://, or *. (for wildcard subdomains)
No Trailing Slashes: Do not include trailing slashes (/) at the end of patterns
Alphanumeric TLDs: Top-level domains (TLDs) can be alphanumeric (e.g., .com, .co.uk, .org)
Optional Ports: Custom ports are allowed (e.g., https://example.com:8080)
Case Insensitive: Patterns are case-insensitive for domain matching
Maximum 10 Origins: You can define up to 10 allowed origin patterns per application
Examples of Valid and Invalid Patterns
| Pattern | Valid? | Reason |
|---|---|---|
| https://example.com | ✅ Yes | Fully qualified domain, no trailing slash |
| http://*.example.com | ✅ Yes | Wildcard subdomain pattern is allowed |
| *.example.com | ✅ Yes | Wildcard without protocol is valid |
| https://example.com:8080 | ✅ Yes | Custom port is supported |
| https://*.example.* | ✅ Yes | Wildcard TLD is allowed |
| http://example.com/ | ❌ No | Trailing slash not permitted |
| https://example | ❌ No | Invalid domain format (missing TLD) |
| *example.com | ❌ No | Wildcard must be properly formatted with dot |
| example.com | ❌ No | Protocol missing (http:// or https:// required) |
Pattern Matching Examples
Below are concrete examples showing how pattern matching works:
| Allowed Pattern | Request Origin | Result |
|---|---|---|
| https://example.com | https://example.com | ✅ Allowed |
| https://example.com | https://sub.example.com | ❌ Blocked (not matching) |
| https://*.example.com | https://api.example.com | ✅ Allowed |
| https://*.example.com | https://example.com | ❌ Blocked (base domain, wildcard requires subdomain) |
| https://*.example.com | https://different.com | ❌ Blocked (different domain) |
| https://*.example.* | https://sub.example.org | ✅ Allowed |
Practical Configuration Scenarios
Scenario 1: Allow All Subdomains
You want to allow your application to be embedded on any subdomain of your company website (e.g., app.example.com, help.example.com, support.example.com).
Allowed Pattern: https://*.example.com
Result: All subdomains of example.com can access resources, but different domains like competitor.com are blocked.
Scenario 2: Restrict to Specific Subdomain Only
You want to allow your application only on your primary web server (app.example.com), blocking all other subdomains and external domains.
Allowed Pattern: https://app.example.com
Result: Only requests from exactly https://app.example.com are allowed. Other subdomains like admin.example.com and external domains are blocked.
Scenario 3: Multiple Environments (Dev, Staging, Prod)
You have three environments and want to allow your application to function in all of them.
Allowed Patterns:
• 1. https://app.dev.example.com (Development)
• 2. https://app.staging.example.com (Staging)
• 3. https://app.example.com (Production)
Result: Each environment can independently access the application with their specific origins. Requests from unlisted origins are rejected.
Scenario 4: Partner Integration with Wildcard
You want to allow your application to be embedded on any subdomain of a partner's website (partner.io).
Allowed Pattern: https://*.partner.io
Result: All subdomains of partner.io can access your application. This is useful for integrations where partners may have different subdomains for different purposes.
How Origin Security Interacts with Other Features
Direct Integration
When Origin Security is enabled, your direct integration script only works when loaded from allowed origins. If your script is embedded on a domain not in your allowed list, the script will not initialize and resources will not load. This is a critical security measure preventing unauthorized use of your integration script.
API Calls
All API calls from your application are validated against the allowed origins list. API requests from non-allowed origins are rejected with a 403 Forbidden error. This ensures that even if someone obtains your API key, they can only use it from approved domains.
Avatar Display
When Origin Security is enabled, the AppNavi avatar is only displayed when accessed from allowed origins. From blocked origins, the avatar remains hidden, providing an additional layer of access control.
Resource Serving
All resources (data files, images, videos, stylesheets) are validated against the allowed origins before being served. Resources requested from non-allowed origins are not served, even if someone has the direct URL.
Related Document
The following features work in conjunction with Origin Security:
• Direct Integration Methods - Overview of direct integration approaches
• Application Settings - Configure all application-level security and integration settings
• UserActivityTracking - Monitor user interactions within allowed origins
• API Security - Protect your APIs with origin-based access control
• Enhance Security - Direct Integration - Additional security features for direct integration
• Integration Troubleshooting - Solve common integration and security issues
Updated 10 days ago